

Microsoft Restricts Employee Use of Anthropic's Claude Fable 5 Over Data Concerns
Microsoft has reportedly limited employee access to Anthropic's newly launched Claude Fable 5 after concerns emerged over the model's data retention and privacy practices. The move signals that enterprise trust and data governance may become the next major battleground in the AI race.
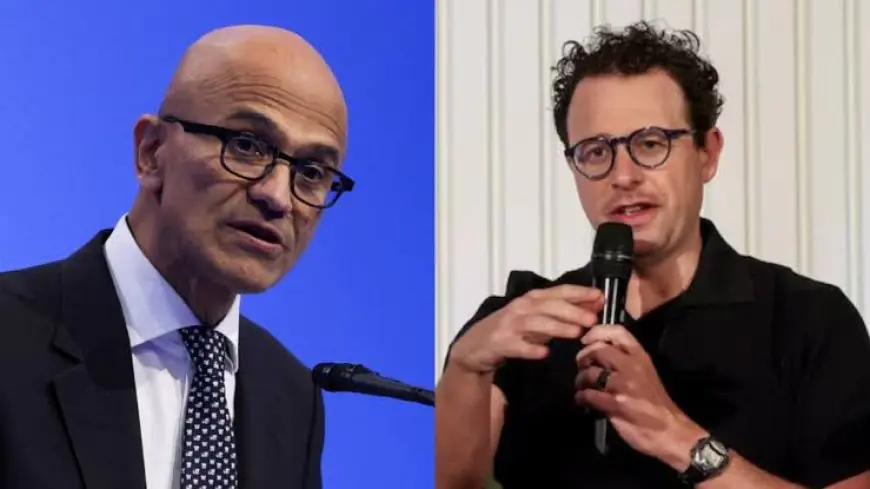

A Warning Shot From Redmond
Microsoft rarely publicly acknowledges competitive threats. But sometimes, actions speak louder than press releases. The tech giant has quietly restricted employee access to Anthropic's newly launched Claude Fable 5, the latest and most powerful model from the OpenAI rival. The reason? Data concerns. According to internal communications viewed by multiple news outlets, Microsoft's legal and security teams flagged potential issues with how Claude Fable 5 handles confidential information, particularly around data retention, logging, and potential use of inputs for model training.
What Exactly Happened
The restrictions came into effect within days of Anthropic's launch of Claude Fable 5. Microsoft employees were initially given access to test the model through Anthropic's API, as part of standard competitive analysis. But according to Reuters reporting on the internal directive, a memo was circulated stating that employees could no longer share "confidential, proprietary, or personally identifiable information" with Claude Fable 5 pending further review. The restrictions stop short of a full ban—employees can still use the model for public or synthetic data—but the message is clear: Microsoft does not fully trust Anthropic with its secrets.
The timing is noteworthy. Anthropic has positioned itself as the trustworthy alternative to OpenAI, with a "Constitutional AI" framework designed to align models with human values. But Microsoft's move suggests that trust is not a checkbox. It is an ongoing negotiation. And when your biggest competitor also happens to be one of your largest enterprise customers, that negotiation gets complicated.
The Specific Data Concerns Explained
So what exactly triggered Microsoft's caution? While Anthropic has not publicly changed its privacy policy for Claude Fable 5, industry sources point to three specific areas of concern:
- Data retention periods – Claude Fable 5 reportedly retains API inputs longer than previous versions, potentially for up to 90 days for "safety and improvement purposes."
- Third-party logging – The model integrates with external monitoring tools that Microsoft's security team has not fully vetted for compliance with internal data handling standards.
- Ambiguous training opt-outs – While Anthropic offers opt-out options for not using customer data for training, Microsoft's legal team found the language less explicit than they require for enterprise agreements.
"We take data security and privacy extremely seriously. We are in active discussions with Anthropic to clarify their practices around customer data. Until those discussions conclude, we have advised employees to exercise caution when sharing sensitive information." – Microsoft spokesperson (statement to Reuters)
The statement is carefully worded. Microsoft is not saying Anthropic did anything wrong. It is saying Microsoft's standards are very high, and Anthropic has not yet proven it meets them. For Anthropic, which counts many Fortune 500 companies as customers, that distinction matters. A direct accusation would be damaging. A "we're still evaluating" signal is merely uncomfortable.
How Anthropic Has Responded
Anthropic has moved quickly to contain the fallout. In a blog post published following the Reuters report, the company clarified that Claude Fable 5's data retention policies are consistent with industry standards and that enterprise customers can request shorter retention windows under custom agreements. The post also emphasized that Anthropic does not train models on customer API inputs without explicit permission, and that all training data is fully anonymized.
But here is the problem: Microsoft's concerns are not about what Anthropic actually does. They are about what Anthropic could do under the current terms of service. Enterprise legal teams do not operate on trust. They operate on contracts. And Microsoft's contract with Anthropic—like most API agreements—gives Anthropic broad discretion to retain and use data unless a customer negotiates specific carve-outs. Microsoft, with its massive negotiating leverage, could probably get those carve-outs. But the fact that it has to ask is the underlying issue.
Comparing Enterprise AI Data Policies
To understand why this matters, it helps to compare how the major AI providers handle customer data. The differences are significant:
| Provider | Default Data Retention | Training on Customer Inputs | Enterprise Opt-Out Available | Third-Party Audits |
|---|---|---|---|---|
| Microsoft (Azure OpenAI) | 30 days (encrypted) | No by default | N/A | Yes (SOC 2, ISO) |
| Anthropic Claude | 90 days (standard) | Opt-out only | Yes (negotiated) | Limited |
| OpenAI (Enterprise) | 30 days | No (enterprise tier) | Yes (standard) | Yes |
| Google (Vertex AI) | 30 days | No | N/A | Yes |
The table shows that Anthropic is not an outlier on default retention. Google and OpenAI have similar policies. But Microsoft's own Azure OpenAI service offers stronger default protections—no training on customer data without explicit permission, shorter retention, and comprehensive third-party audits. When Microsoft employees use Anthropic's model, they are stepping into a less protective environment than the one Microsoft provides its own customers. For a company that markets itself as a trusted steward of enterprise data, that inconsistency is unacceptable.
The Anchor What This Means for Enterprise AI Buyers
For technology leaders evaluating AI vendors, the Microsoft-Anthropic dustup is a wake-up call. The Gartner enterprise AI data governance framework (anchor link) emphasizes that data handling policies should be a primary evaluation criterion, not an afterthought. Too many procurement teams focus on model performance benchmarks and ignore the legal and compliance implications of where their data goes and how it is used. Microsoft's action demonstrates that even sophisticated buyers can get caught off guard.
The lesson is not that Anthropic is unsafe. The lesson is that "safe enough for general use" and "safe enough for Microsoft's internal secrets" are different standards. Enterprises need to decide which standard applies to their own data. For non-sensitive workloads, Anthropic's policies are likely fine. For confidential financial data, trade secrets, or personal customer information, enterprises should negotiate custom agreements or choose vendors with stronger default protections.
The Competitive Implications
Microsoft's restriction is also a competitive shot across Anthropic's bow. Microsoft has invested over $13 billion in OpenAI and integrates OpenAI's models deeply into its product stack. It has every incentive to make competing models look riskier by comparison. Whether the data concerns are genuine or pretextual is almost impossible for outsiders to determine. But the effect is the same: enterprise buyers now have a reason to hesitate before standardizing on Claude.
As noted in a Wall Street Journal analysis of the growing AI data privacy battle, this is likely the first of many such skirmishes. As AI models become more powerful, the data they ingest becomes more valuable. And the companies that control that data—both the AI providers and their enterprise customers—will increasingly clash over who owns what, who can see what, and who is liable when things go wrong. Microsoft is simply the first major player to draw a line in the sand.
What Anthropic Needs to Do Now
Anthropic's path forward is clear but not easy. It must re-engineer its data governance practices to meet the highest enterprise standards, not just industry averages. That means shorter default retention (30 days or less), explicit "no training on customer data" terms without requiring opt-out, and third-party security audits that it publishes publicly. These changes are costly and operationally complex. But they are also the price of competing for the largest enterprise accounts.
Anthropic has built its brand on being the responsible AI company. Microsoft's action challenges that brand directly. How Anthropic responds—defensively or transparently—will determine whether this incident is a temporary setback or a lasting reputational wound.
How Best Can This Be Handled
The Microsoft-Anthropic situation is not going away. Both companies are likely in active negotiations to clarify data handling terms. A revised enterprise agreement that addresses Microsoft's concerns could be announced within weeks. But the broader message to the industry is already clear: data governance is not a "nice to have" feature for enterprise AI. It is the feature. The model that performs best on benchmarks but cannot satisfy corporate legal teams will not win the enterprise market. And the companies that treat data privacy as a competitive differentiator rather than a compliance burden will have a genuine edge.
For now, Microsoft has sent a signal. Anthropic has heard it. And every other AI provider is watching closely. The AI race just added a new dimension: trust. And trust, unlike model accuracy, cannot be patched overnight.